Knowledge should leave with receipts
Portable knowledge is not just export. It needs provenance, shape, policy, and verification details that travel with the bundle.
Most knowledge tools have an export story.
Download the notes. Export the database. Sync the files. Dump the markdown. Save the attachments.
That can be useful. It is not the same as ownership.
The harder question is what happens after the export lands somewhere else. Can another system tell where the knowledge came from? Can it separate the original source from the summary? Can it prove which attachment belongs to which note? Can it distinguish version one from version six? Can an operator audit the path from evidence to conclusion?
If not, the organization may have the data but lose the receipts.

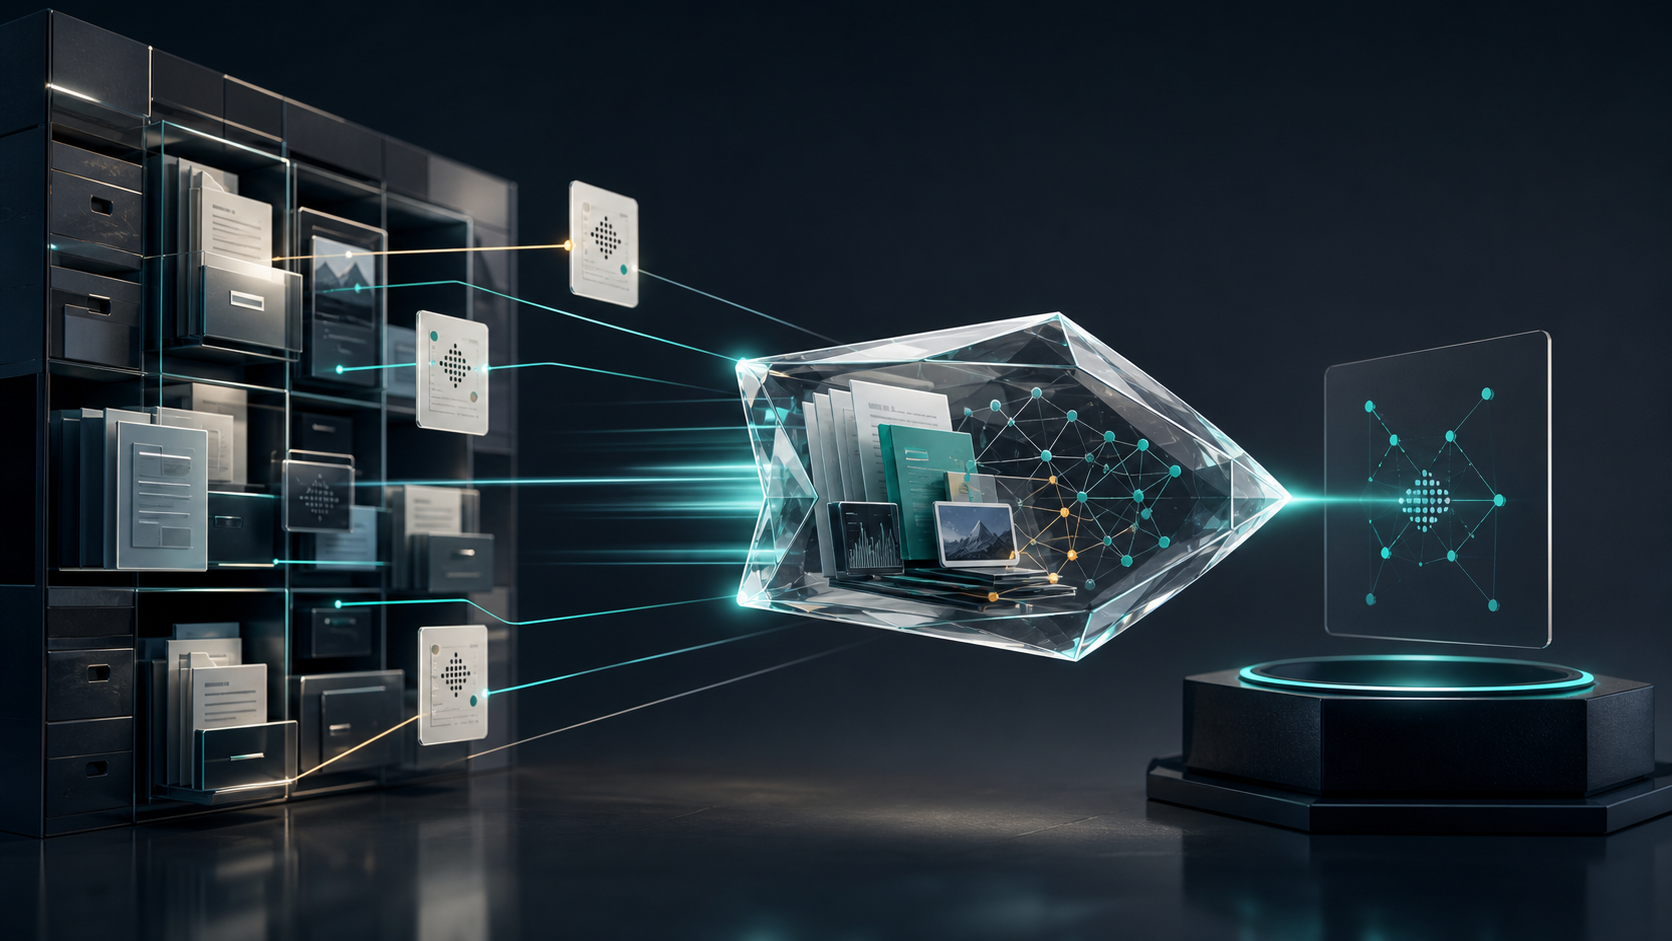
Illustrative receipt structure: provenance, manifest, policy, and verification metadata travel beside the content so portability can be inspected.
Run the receipts test
Choose one important knowledge bundle.
Make it concrete: a decision record, research packet, incident note, product brief, customer finding, architecture recommendation, or agent-generated synthesis that someone may need to trust six months from now.
Now ask eight questions.
1. Is the original source record included or clearly referenced? 2. Are attachments carried with stable identifiers instead of loose filenames? 3. Can you verify that the attachment is the same file that was reviewed? 4. Is the first version preserved? 5. Are revisions distinguishable from the original? 6. Is the relationship between source, extraction, summary, and decision visible? 7. Is there a manifest, checksum, or equivalent receipt that can be checked after transfer? 8. Can another system import the bundle without flattening away the evidence trail?
If the answer is mostly “no,” the export is a copy. It is not portable knowledge.
Export is not ownership
Export answers a narrow question: can the material leave the application?
Ownership asks a wider question: can the material remain useful, attributable, and inspectable after it leaves?
That difference matters because knowledge is rarely one clean object. It is usually a bundle:
- the note someone wrote;
- the source document or media that informed it;
- the attachment that must not be silently swapped;
- the generated extraction or summary;
- the later correction;
- the person, agent, or process that changed it;
- the decision that depended on it.
A flat export can preserve the words while losing the structure that made the words trustworthy.
That is how lock-in becomes subtle. The data may be technically accessible, but the meaning still depends on the original application.
Receipts make portability inspectable
A receipt is not marketing language. It is evidence that travels with the bundle.
For knowledge systems, the receipt can include:
- stable identifiers for records and attachments;
- content hashes or other integrity checks;
- immutable version references;
- provenance links between source, transformation, and result;
- a manifest that says what the bundle contains;
- import/export behavior that preserves those relationships;
- access and encryption boundaries for sensitive material.
The point is not to make every note heavy. The point is to protect the material that future work may rely on.
If an agent will use a research summary to write a recommendation, the summary should still know which sources shaped it. If a team exports a decision packet during a migration, the packet should still show which attachments were reviewed. If a compliance-sensitive workflow changes a record, the old state should not vanish behind the new one.
Without receipts, the next system has to trust the export by assumption.
The receipt needs to travel with the knowledge
Many tools can show history while you remain inside the tool.
That is useful, but it is not enough for portability. The test is what survives outside the original boundary.
Can a teammate open the bundle later and see the source chain? Can an external process verify that the media file matches the recorded attachment? Can an importer preserve the difference between raw source, extracted text, derived summary, and human decision? Can an operator see why a claim exists without reconstructing it from memory?
This is where “own your data” needs a stricter standard.
Owning the final text is weaker than owning the knowledge package. The package should carry enough evidence for another system to reason about it without pretending the original app is still present.
Fortemi treats the package as the product surface
Fortemi is positioned as an intelligent database for AI-ready applications: knowledge management, RAG, agent memory, team documentation, and related workflows built on a normalized, provenance-aware substrate.
The relevant idea for this campaign is not a generic claim that Fortemi stores things. It is the packaging model.
Fortemi’s architecture materials describe notes that can carry arbitrary content, content-addressed attachments, versioning and hashes, provenance tracking, portable Knowledge Shards, identity and encryption boundaries, and import/export behavior. In the public repository, Fortemi also presents the broader substrate around ingestion, extraction, graph/search surfaces, API/MCP access, and provenance-aware structures.
That combination gives builders something specific to inspect:
- Does the knowledge object keep its attachments tied to the record?
- Does a versioned record remain distinguishable after change?
- Does provenance survive as a first-class relationship?
- Does the export model carry a manifest instead of only a text dump?
- Does the import path preserve the bundle rather than flatten it?
Those are better questions than “does it export?”
They turn portability from a slogan into an engineering property.
What not to claim
A receipt is not a magic trust layer.
It does not prove that a source was accurate. It does not prove that a summary was correct. It does not replace review, governance, access control, or compliance work. It does not show performance, reliability, adoption, or business value by itself.
It answers a narrower but important question: can the system preserve the evidence needed to inspect the knowledge later?
That is enough for the campaign.
Fortemi should be evaluated as a concrete substrate for verifiable knowledge packages, not as a vague promise that all memory becomes trustworthy.
Start with one bundle
Do not redesign the whole knowledge stack first.
Pick one bundle that already matters. Write this sentence:
This knowledge is portable only if another system can verify [source], [attachments], [versions], [provenance], and [integrity receipt] after export.
Then test the system you already use.
If it passes, keep using it. If it fails, the gap is now precise: the data can leave, but the receipts cannot.
That is the right moment to inspect Fortemi as one implementation model for knowledge that leaves with evidence attached.